The question
Europe's AI rulebook asks independent evaluators to verify that the most powerful AI models are safe — before the public relies on them. But today, an external evaluator examining a frontier model gets a chat window and an API key: they can knock on the front door and note what comes out. They cannot look inside. Research has shown that this black-box testing can miss precisely the things that matter most — hidden capabilities, backdoors planted during training, "deleted" abilities that were never really removed.
Why not simply hand evaluators the model? Because a frontier model's weights are its maker's most valuable asset and, for the most capable systems, a security risk if leaked. For years this stand-off looked unsolvable: real scrutiny or real security — pick one. The practical consequence was that "independent evaluation" risked meaning little more than checking a company's homework using the company's own pencil.
The breakthrough — and why it is only possible now
Confidential computing dissolves the trade-off. Modern processors can create a hardware-sealed environment — a trusted execution environment — that is locked even against the person who owns the machine. The hardware can also produce a cryptographic certificate (attestation) proving exactly which code ran inside. Put an AI model and an evaluator's tests inside such an environment and something new becomes possible: the evaluator works directly with the model's internals, while the developer's weights never leave the sealed hardware. Only the evidence — bounded, signed results — comes out.
And it protects both sides at once. The developer cannot see the evaluator's test suite — so tests cannot be studied and gamed, and the evaluator's methods stay confidential. The evaluator cannot copy the model. Each side keeps its secrets; both can trust the result. It is the digital equivalent of a double-blind procedure, and that mutual guarantee is what makes deep audits acceptable to the audited as well as the auditor. In August 2026, this stopped being theory: OpenMined's PySyft powered the world's first double-blind evaluation of a proprietary frontier model, together with Google DeepMind, the Singapore AI Safety Institute, MLCommons and AVERI — and it will be presented first-hand at this event.
Why didn't this happen years ago? Three things had to converge, and the third arrived only in the last few months:
- The hardware. Secure enclaves have existed in ordinary CPUs for a decade — but only for small workloads. Frontier AI runs on GPUs, and GPU-scale confidential computing has only become available in the latest generation of AI accelerators.
- The regulatory demand. Until recently, no legal framework asked for evaluations deep enough to need this machinery. That has changed — and not only for general-purpose AI under the AI Act and the GPAI Code of Practice. Member States are standing up their own evaluation capacity: France inaugurated INESIA, its national institute for AI evaluation and security, in 2025; Spain created AESIA, its AI supervision agency; counterparts are emerging in Germany, Italy and beyond, alongside the EU's AI Office. Every one of these bodies faces the same access problem this technology solves.
- The proof it's affordable. Everyone assumed sealing a giant model inside secure hardware would be cripplingly slow. Nobody had publicly measured it — until now.
These are the first public measurements of their kind, and they change the default answer. The obstacle to deep, independent AI audits is no longer physics or economics — it is institutional design. That is a question for policymakers, and it is now an open one.
Why it matters — whether you regulate, build or watch AI
- It turns "trust us" into "verify". Safety claims about frontier models — closed and open-weight — can be independently checked before public release, not taken on faith from the provider.
- It makes the AI Act enforceable in practice. Obligations on paper need technical means. Verification infrastructure is to AI governance what emissions testing is to car regulation.
- It is technological sovereignty in practice. A European capability to verify — rather than a dependency on providers' self-assessments — built on open research, relevant to the Cloud and AI Development Act and Europe's AI Gigafactories.
- Model providers gain too. Because their weights stay protected, providers can bring in outside evaluators and red-teamers during development, not just at the finish line — catching problems earlier and making external scrutiny a routine part of building a model rather than an adversarial event at the end.
- It makes compliance with EU digital law easier to demonstrate. The sealed hardware produces a cryptographic certificate of exactly which tests ran on which system, and results leave as tamper-evident, signed evidence. Compliance stops being a paper promise and becomes something a regulator can check. The same mechanism serves the AI Act's model evaluations, the Digital Services Act's vetted-researcher access to platform data, the GDPR when evaluations touch personal data, and the secure processing environments required by the Data Governance Act and the European Health Data Space.
- It protects innovation too. The same guarantees that let an auditor probe a model let hospitals, banks and statistics offices collaborate on data they could never share. Scrutiny and competitiveness are the same infrastructure.
The natural next step, which the keynote will put on the table: a European pilot joining an evaluator body, a governance partner and a frontier lab.
Speakers
Koen van der Veen is an Engineering Manager at OpenMined focused on building secure, privacy-preserving systems and infrastructure. He works on PySyft, with a particular interest in confidential computing, distributed systems, and tools for working safely with non-public data. His work spans system design, cloud infrastructure, developer tooling, and applied AI, with an emphasis on making complex security and privacy guarantees practical for real-world applications.
Talk — Double-blind evals in practice: evaluating private frontier AI on private safety benchmarks. OpenMined recently built the world's first double-blind evaluation of a proprietary frontier AI model, enabling independent evaluation while keeping both the model and the benchmark confidential. This talk explains how the system was built and the technical architecture that makes it possible — including the key challenges around confidentiality, trust, governance, and verifying what actually runs inside the secure environment.
Dr Alejandro Tlaie Boria leads OpenMined's AI-audits stream (from September 2026). He conducted the research presented at this event as AI Policy Advisor at Pour Demain, working on AI verification: securely enabling deeper-than-black-box third-party evaluations of frontier models. Previously a Talos Fellow at SaferAI quantifying AI cyber-risk, he has around ten years of research experience (PhD, two postdocs, MPhil).
Key publications: Securing External Deeper-than-Black-Box GPAI Evaluations · A Blueprint for an EU Ecosystem of Secure, Deep and External AI Audits · Confidential computing can enable better frontier AI auditing · Don't Let AI Audits Become a Box-Ticking Exercise
On the panel — open Q&A and discussion (16:55): the EU AI Office’s Kristijonas Čyras and Gökhan Önel join the discussion with the audience alongside the speakers, for questions touching on the role of the AI Office and the AI Act framework for general-purpose AI models.
Kristijonas Čyras is a technology specialist with the EU AI Office’s AI Safety Unit (European Commission). He works on assessing general-purpose AI model provider compliance with the EU AI Act, with a focus on the third-party evaluator ecosystem. He previously researched safe and explainable AI at Ericsson (California, USA and Sweden) and Imperial College London (UK).
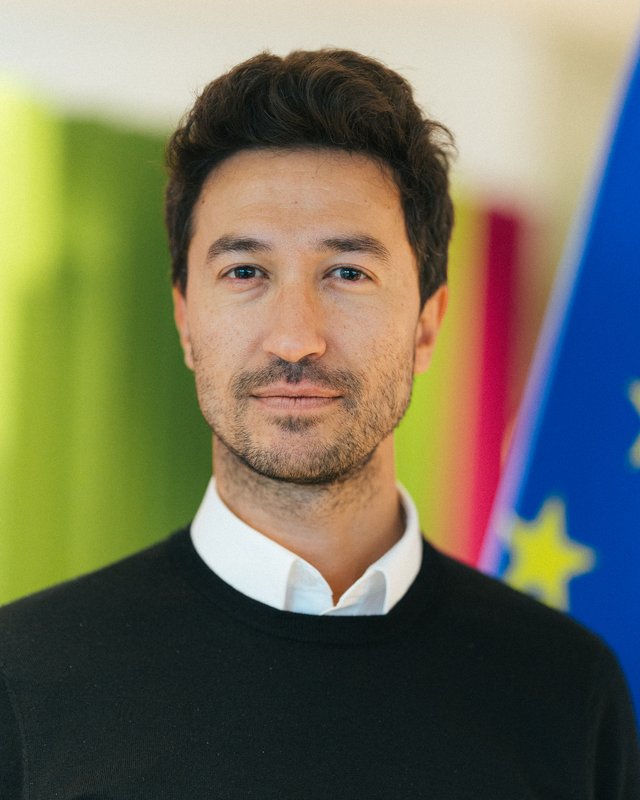
Gökhan Önel is a technology specialist with the EU AI Office’s AI Safety Unit (European Commission). He works on assessing general-purpose AI model provider compliance with the EU AI Act, with a particular focus on post-market monitoring and harmful manipulation risks. He was previously Head of Data Analytics at Meta’s Trust & Safety department.
Programme (16:00–18:30)
The session is chaired and moderated jointly by the OpenMined Foundation and Pour Demain Europe. The European Commission’s EU AI Office joins the panel discussion.
| 16:00 | Opening — welcome and framing by the co-chairs, OpenMined Foundation & Pour Demain Europe |
| 16:10 | Why this research matters — the Pour Demain perspective |
| 16:15 | Double-blind evals in practice — evaluating private frontier AI on private safety benchmarks, Koen van der Veen (OpenMined) |
| 16:25 | Keynote — Enabling Better AI Audits with Privacy-Enhancing Technologies, Dr Alejandro Tlaie |
| 16:55 | Open Q&A and panel discussion — the speakers, joined by Kristijonas Čyras and Gökhan Önel (European Commission, EU AI Office); moderated by the co-chairs |
| 17:25 | Closing — by the co-chairs |
| 17:30 | Networking reception — until 18:30 (optional) |
Who should attend
The event is open to the public — anyone interested in how Europe will verify the safety of advanced AI is welcome; registration is free. It will be of particular interest to:
EU policymakers and staff (European Commission / AI Office, Members of the European Parliament and their advisers, Member State digital ministries) · AI Safety and Security Institutes and notified bodies · general-purpose AI model providers and compliance teams · third-party evaluators, auditors and red-teaming firms · confidential-computing and PET vendors · civil society and academia working on AI accountability · press covering AI governance.
Registration
Registration is a two-step process: after submitting, you receive an email with a confirmation link — your registration (and your seat, for in-person attendance) becomes final when you click it. Only one registration per email address is possible; the confirmation email also contains your personal links: to see the participant list, to cancel, or to stop sharing your details with other participants. In-person seats are limited: once capacity is reached, further confirmations join a waiting list (you are notified either way by email). Online participation has no limit — the connection link is emailed before the event. Registrations close on Thursday 12 November 2026, 18:00 (to be confirmed).
Your details are used solely for organising this event and are deleted no later than 30 days after it (unless you opt in to updates — see the privacy notice below). If the venue requires security accreditation, confirmed in-person attendees will be asked separately for the necessary ID details.
Privacy notice — how your data is handled
Who we are. Registration for this event is organised by the OpenMined Foundation (New York, USA) and Pour Demain Europe ASBL (Brussels, Belgium), acting as joint controllers. Contact for anything concerning your data: events@openmined.org.
What we collect and why. Your name, organisation/function, email address and how you attend (in person or online) and whether you plan to stay for the reception — solely to organise this event: managing registrations, seats and the waiting list, and sending you the registration emails described on this page (legal basis: steps taken at your request for your participation). Only if you tick the sharing box, your name and organisation are made visible to the other registered participants (legal basis: your consent, withdrawable at any time via the link in your confirmation email).
Staying informed (optional). Only if you tick "Keep me posted on OpenMined's work", we also use your name and email address to send you occasional updates about OpenMined's work after the event (legal basis: your consent). You can withdraw this consent at any time — simply reply to any of our emails or write to the contact above — and withdrawing it does not affect your event registration. Cancelling your event registration also ends these updates. If you do not tick the box, nothing is kept beyond the retention period below.
Who processes it. Data is stored and emails are sent through Google Workspace (Google Sheets and Gmail), with Google acting as processor under OpenMined's agreement with Google; Google's EU–US Data Privacy Framework certification covers the related transfers. The full registration list is accessible only to the organising team. The participant list is accessible only to confirmed participants through a personal link, and shows only those who consented.
How long. All registration data is deleted no later than 30 days after the event (by 16 December 2026) — with one exception: if you ticked "Keep me posted on OpenMined's work", we keep your name and email address (nothing else) for that purpose until you unsubscribe. If you cancel, your details are kept only until the event for administrative purposes and then deleted with the rest.
Your rights. You can access, correct or delete your data, or withdraw your consent, at any time: the cancel and stop-sharing links in your confirmation email take effect immediately, or write to the contact above. You may also lodge a complaint with your data protection authority (in Belgium: the APD/GBA).